Security and governance
Built for work that cannot live in a shared password manager.
TheStakk puts isolation, credential handling, permissions and execution history around every application and every workspace from the start.
Core controls
Security is part of the product architecture.
Not a layer added before procurement asks. These controls exist in every deployment, on both commercial routes.
7 controls · every workspace
Encrypted Vault
Client credentials encrypted at rest, never surfaced in logs or interfaces.
Tenant isolation
Strict separation of clients, data, inputs and results. Enforced at database level.
Role-based access
Control who can run apps, manage credentials and view results, per workspace.
Audit trail
Full execution history, per client, exportable.
GDPR & EU AI Act
European infrastructure, documented data processing, transparency obligations handled by default.
Account security, the serious kind
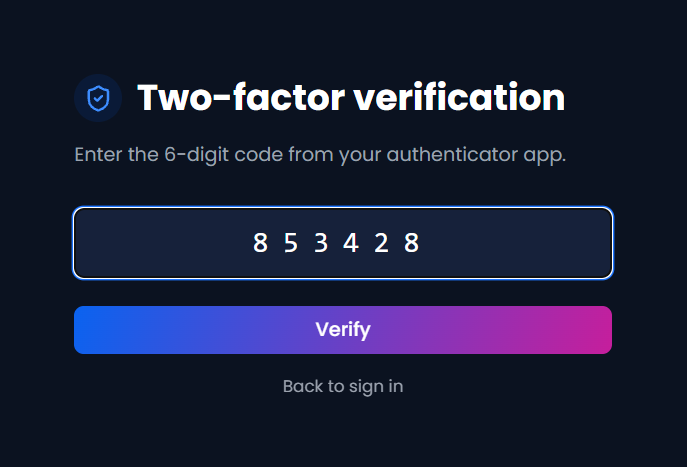
Two-factor authentication (TOTP), active session management with remote sign-out, and a full trail of who did what, when, in every workspace.
Locked-down integrations
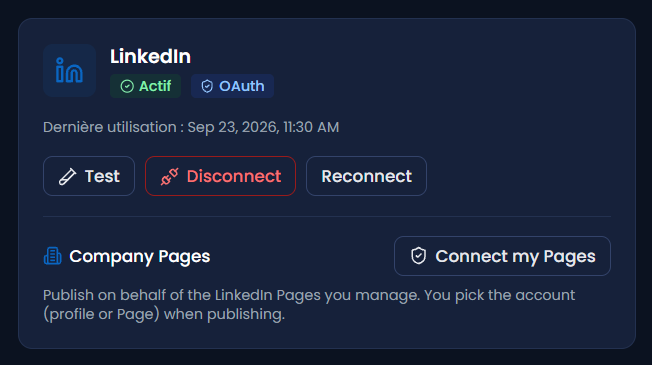
OAuth connections with verified scopes, API keys restricted per endpoint with IP allow-lists, per-key quotas, and one-click revocation. Third-party access is granted narrowly and revoked instantly.
Data flow
What happens from connection to result.
Published commitments